Choose a tab. Open a case.
Hi, I’m Jack.
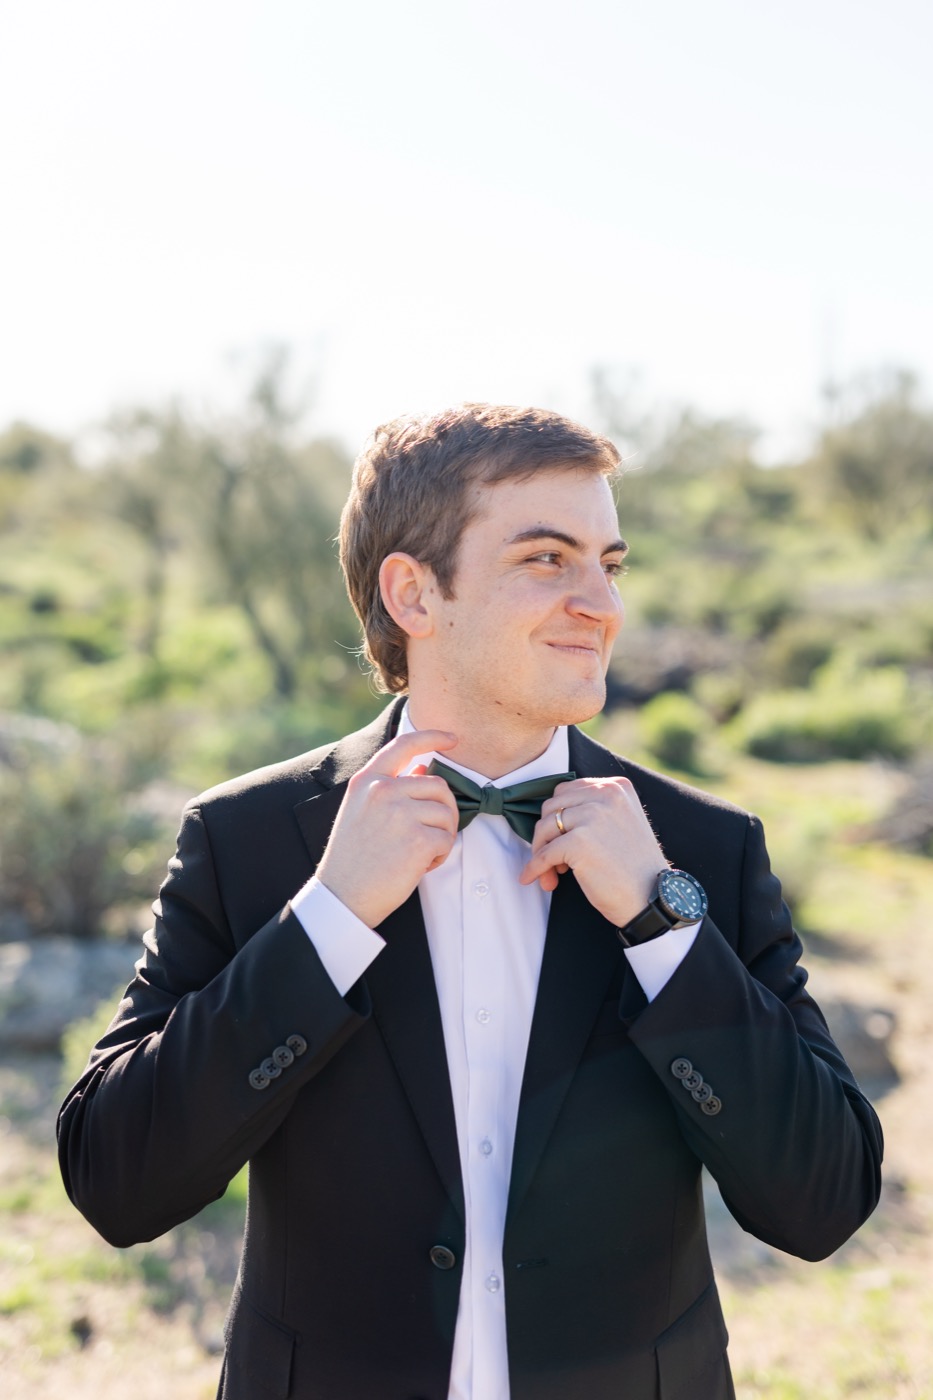
A LITTLE ABOUT ME
Security
engineer.
I build tools, investigate systems,
and write down what I learn.
Curiosity comes with the job.
Close to the systems.
My day-to-day work is security infrastructure: telemetry, access, automation, and the systems teams depend on. Outside that, I build independent tools and write about AI agents, deployment decisions, and what I learn by testing things.
Explore my experience
Independent work.
Tools I’ve built, and the decisions behind them.
iscooked
A practical look at the exposed listeners, permissions, and configurations around self-hosted AI.
Open case
LLM Scout
Separating model quality from hardware fit—and documenting the ranking when the service retired.
Open caseBuild it. Test it. Keep the notes.
What’s exposed?
iscooked — Security scanning for self-hosted LLM deployments.
INDEPENDENT SECURITY TOOL
Local doesn’t
mean private.
A scanner for the listeners, permissions, and configurations around self-hosted AI.
Know what’s exposed.
Know what’s still unknown.
Inside the checks
- Service listeners & API authentication
- Container privileges & file permissions
- Agent settings & inspection limits
Checks report scoped findings. Unknown or skipped checks do not establish safety.
Will it actually run?
LLM Scout — Model quality, hardware fit, and the difference between them.
LOCAL AI / SYSTEM DESIGN
A good model.
For your machine.
I built Scout to separate model quality from hardware fit. Then documented the reasoning when I retired it.
One score can’t
answer every question.
Inside the ranking
- Quality: what the evidence says
- Hardware fit: what can actually load
- Best Fit: ranking the models that pass
What I’ve done.
Security infrastructure, automation, and AI research.

Threat Infrastructure Senior Cybersecurity Engineer
Own architecture and delivery for a Databricks-based AWS Security Data Lake and Databahn rollout, spanning endpoint telemetry, role-based access control, disaster recovery, and downstream analytics.
- Led Databahn endpoint telemetry implementation for 70,000+ endpoints, preserving ingestion quality, access control, and recovery design.
- Drove planning, architecture decisions, stakeholder alignment, and delivery sequencing across security engineering, vendor teams, and platform owners.
- Built GitLab CI/CD promotion gates, Tanium REST API workflows, Sysmon deployment automation, access reviews, and JIRA remediation pipelines.
AI agent infrastructure security
Researched self-hosted AI agent stacks, including local model runtimes, shell and environment access, tool permissions, prompt boundaries, and control-plane exposure. Mapped the work against OWASP LLM Top 10, NIST AI RMF, and MITRE ATLAS; investigated indirect prompt injection through environment-variable exposure.
Read the field noteAreas of work
AI & application security
Threat modeling, secure design review, agent permissions, indirect prompt injection, vulnerability remediation.
Security data platforms
Databricks, Databahn, AWS, endpoint telemetry, RBAC, disaster recovery.
Automation & delivery
Python, REST APIs, GitLab CI/CD, Tanium, Sysmon, access reviews, JIRA workflows.
Education & certifications
2026
M.S. Cybersecurity and Information Assurance
Western Governors University
2020
B.S. Economics
Arizona State University
CompTIA PenTest+ / CompTIA CySA+ / CompTIA Network+
Leave a paper trail.
Engineering notes — Decisions, tradeoffs, and the evidence behind them.
A real AI-assisted production cutover.
With guardrails.
Human approval. Rollback ready. Evidence first.
I shut down LLM Scout.
Here’s how the ranking worked.
Quality, hardware fit, and why they aren’t the same.
AI is not here to
replace your brain.
Keep ownership of the thinking.
I gave an LLM shell access to a server.
Here’s what I learned.
Agent hardening, shell access, and what held up under testing.
The reasoning is part of the work.